Speaking
Who sees your data before your model does?
Securing the human layer of AI under DPDP
CyberX 2026 · Counterstrike · Garnet × CIOAxis · 9 October 2026 · Taj Yeshwantpur, Bengaluru
Speaking as Fractional COO & GTM Lead, LabelFort (by Predusk AI)
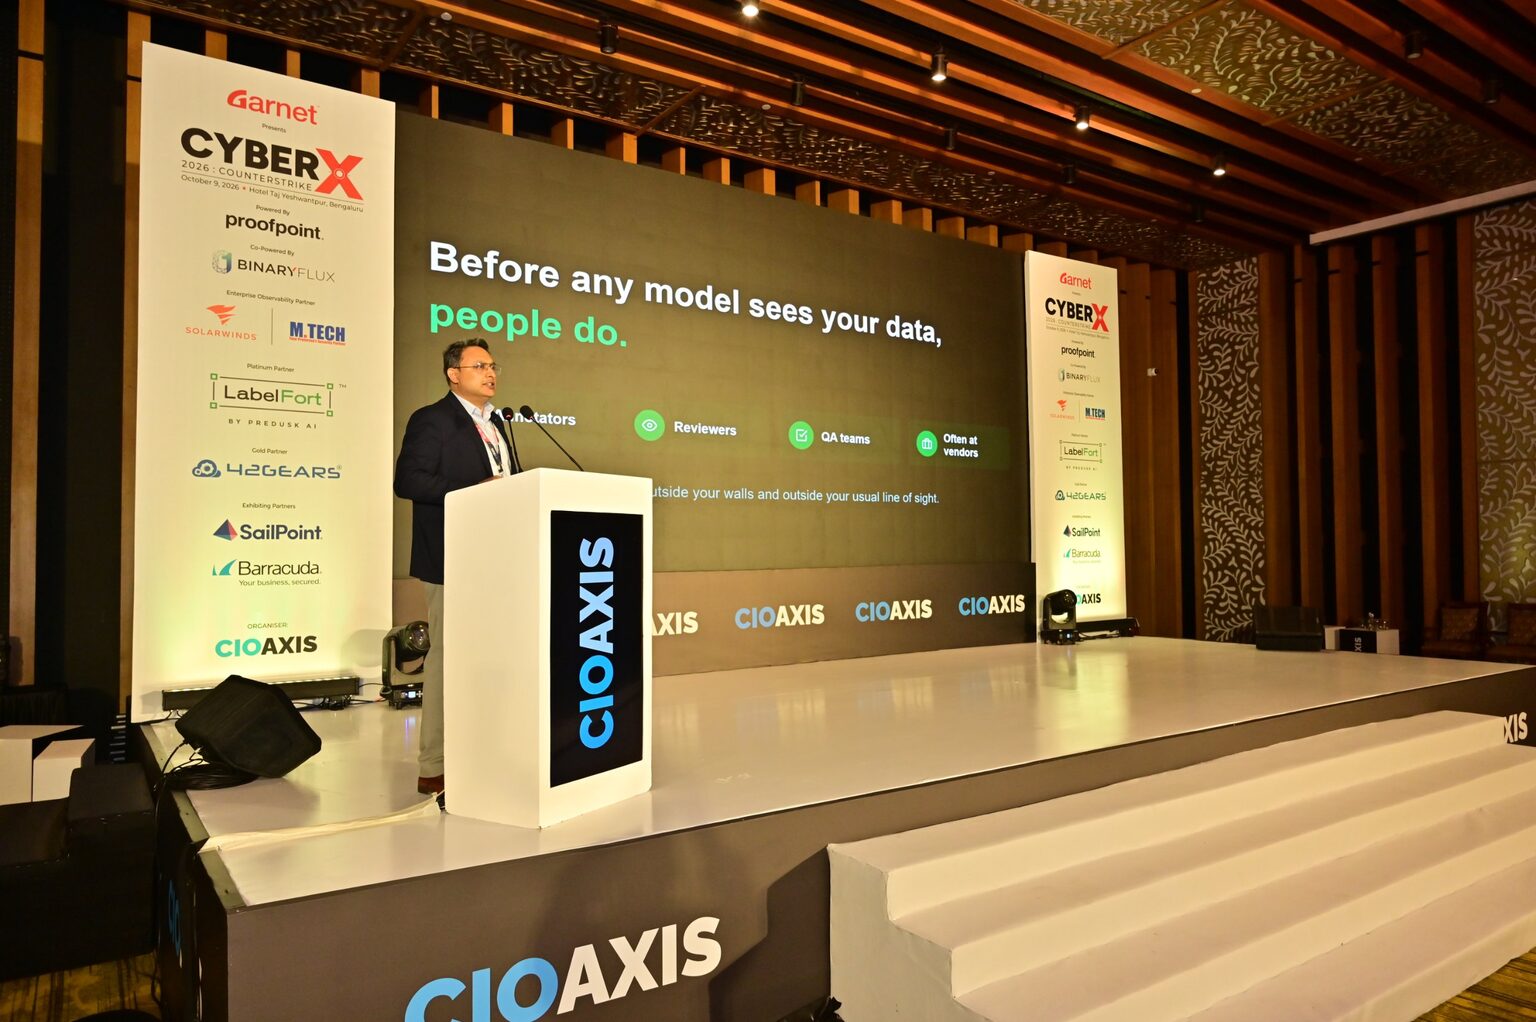
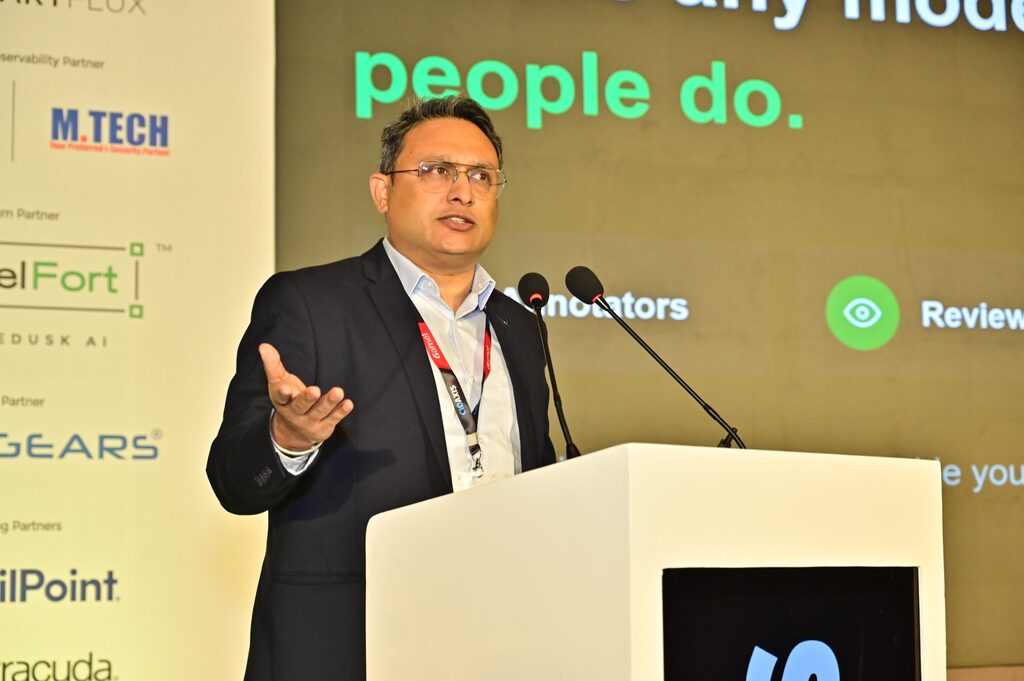
Photos: CIOAxis
The argument
Before any model sees your data, people do: annotators, reviewers and QA teams, often working for a vendor, outside your walls and outside your usual line of sight. For most security programmes this human layer is a blind spot. Annotation vendors are onboarded as services partners rather than reviewed as processors of personal data, labelling usually needs the unmasked original, and the work spreads across people, shifts, tools and subcontractors the buyer rarely sees.
Four questions for every training record
From where?
Under which consent?
Can it be erased, including every copy?
What good looks like: five controls
Access
named users, role-based, least privilege
Visibility
every view and edit logged per record
Containment
isolated workspaces, no local copies
Lifecycle
purpose tagged, retention set, deletion verified
Location
know where every reviewer sits, subcontractors included
Governed data is better data. The controls a CISO wants are the ones an AI team needs.
Why now
Under India's DPDP Act, failing to take reasonable security safeguards can attract penalties of up to ₹250 crore, and those safeguards extend to your vendors. Core obligations become enforceable in May 2027.
DPDP Act 2023, Schedule; DPDP Rules 2025. Not legal advice.
Speaking
Start a conversation Invite Chirayu to speak
On operating discipline, AI ops governance, GCC scale and DPDP readiness for outsourced operations.